Enterprise IT
Security monitoring, event correlation and investigation across enterprise systems and digital infrastructure.
Terrastrium brings together the AI-driven security operations and industrial security to address cybersecurity across enterprise IT, operational technology and industrial control systems. Through Spharaka Sphere™ and Spharaka Signal™, organisations can explore a connected approach to threat detection, investigation and governed response.
Security monitoring, event correlation and investigation across enterprise systems and digital infrastructure.
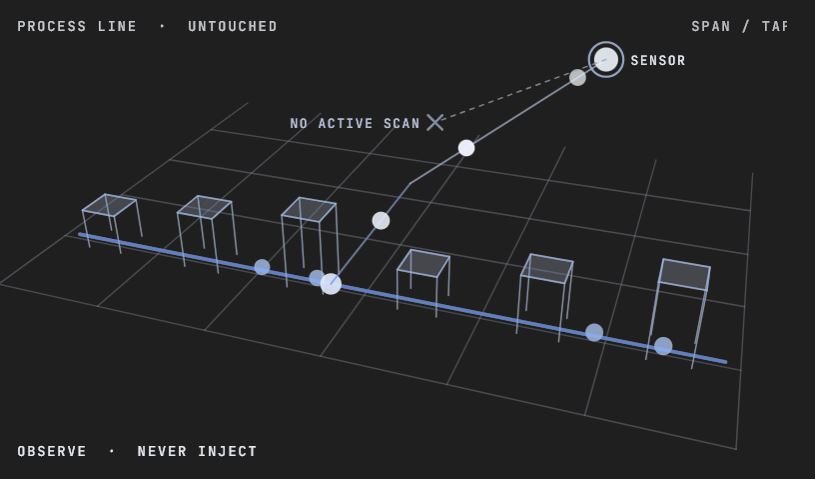
Industrial network visibility and threat detection designed around operational continuity.
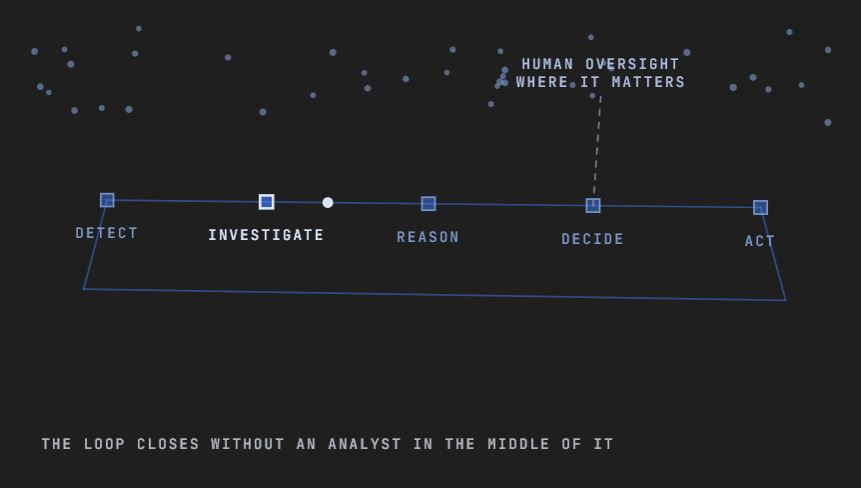
Connect relevant security signals to support investigations across IT and industrial environments.
Enterprise IT and industrial environments have different security and operational requirements. Sphere and Signal address complementary parts of this landscape.
Sphere brings together security monitoring, investigation and response capabilities to help teams correlate alerts, develop incident context and coordinate security workflows.
Signal addresses industrial security requirements through OT network visibility and industrial context, supporting the investigation of suspicious activity in operational technology and industrial control environments.
Bring security data and investigation workflows together to improve context, reduce fragmented investigations and support appropriate response decisions.
Correlate events from supported security data sources to identify related activity and provide context for investigation.
Coordinate investigation tasks, gather relevant evidence and help analysts develop a more complete understanding of potential incidents.
Support response workflows within defined policies, approval requirements and organisational controls.
Use behavioural context and correlated signals to help identify suspicious activity across supported systems.
Bring together supported endpoint and security telemetry to provide a more connected view of potential incidents.
Enrich investigations with available threat intelligence and support searches for suspicious activity across accessible telemetry.
Industrial environments require a security approach that considers production availability, process integrity and operational safety. OT and ICS security focuses on the devices, communications and control systems supporting industrial processes.
Develop visibility into industrial devices and observed network relationships, subject to the supported monitoring capabilities and site architecture.
Establish visibility into observed communications between industrial devices and network segments to help identify unexpected activity.
Support investigation of cybersecurity events affecting industrial control environments, with attention to the operational context of connected systems.
Sphere's AI-native investigation approach is designed to connect security context, coordinate specialised analysis and support governed response rather than relying exclusively on isolated alerts and manual investigation.
Spharaka's cybersecurity-specific AI model, designed to support security reasoning and investigation workflows.
Multi-agent orchestration designed to coordinate specialised AI agents across connected security investigation tasks.
A governance layer designed to validate autonomous actions against defined policies before execution.
Cyber incidents can cross the boundary between enterprise networks and industrial environments. Bringing relevant security information into a connected investigation can help teams understand potential relationships between events and assess their operational significance.
Sphere supports enterprise security investigation, while Signal provides OT and ICS security context. Where supported integrations are available, this complementary approach can help organisations investigate potential attack paths, correlate relevant evidence and coordinate response decisions across IT and operational environments. Actions affecting industrial systems should follow appropriate operational approval and safety procedures.
Deployment options, integration scope and infrastructure requirements should be assessed against your organisation's security architecture, data policies and operational needs.
Explore deployment within customer-managed infrastructure, subject to platform requirements and compatibility.
Discuss disconnected or tightly controlled deployments where supported by the relevant platform configuration.
Assess compatible log sources, security tools, industrial telemetry and integration requirements for the intended deployment.
Our technology initiatives are connected to deep-tech innovation, artificial intelligence and indigenous technology development.
Deep-tech ecosystem affiliation supporting technology innovation and development in India.
Part of AI-focused startup programme supporting innovation and technology development.
Association with a national Centre of Excellence initiative supporting technology development.
Class A certification for indigenous technology.